Read-only AWS audit · 7 scanning engines · zero agents

Zero agents.
Cloud waste, revealed.

Nothing hidden. Nothing touched.
We read the metadata your cloud already tells the truth in — and never the data itself.

GhostTrace analyzes metadata — never your files or workloads — to uncover unattached storage, idle compute, abandoned databases, and security drift across your AWS account.

No credit card Read-only IAM Zero disruption Report in under 3 min
ghosttrace inspect · audit engine read-only
12:04:02Connected via STS AssumeRole (acct 847…312)
12:04:05Enumerating 426 resources (S3, EBS, EC2, RDS)…
12:04:12FINDING · 14 unattached EBS volumes · $5,100/yr
12:04:18FINDING · 9 zero-connection RDS instances
12:04:21Correlating spend · storage class · attachment state
12:04:23Audit complete · report generated
Scanning estate
ESTIMATED ANNUAL SPEND $64,820
RECOVERABLE WASTE $12,450 / yr
20–35%
of a typical AWS bill is recoverable waste
7
services audited from one read-only role
$0.00
of object or row data ever read
<180s
from connect to a costed audit report
Why metric tools miss it

Metrics guess.
Metadata proves.

Standard tools read CPU percentages and demand downsizing. GhostTrace checks listener ports, attachment state, and cross-service dependencies first — then quantifies the finding in dollars and ranks it by impact. One read-only role reads every layer: storage, compute, database, serverless, logging, and the plumbing between them.

Deterministic, not speculative

Findings and savings are computed by pure functions from explicit metadata facts — attachment state, listener ports, pricing tiers, storage classes, connection counts. Reproducible and auditable, with overlapping optimizations de-duplicated so no dollar is counted twice.

  • Dollar-quantified waste per bucket, volume, instance, and database
  • gp2→gp3 migration impact and unattached-volume billing exposure
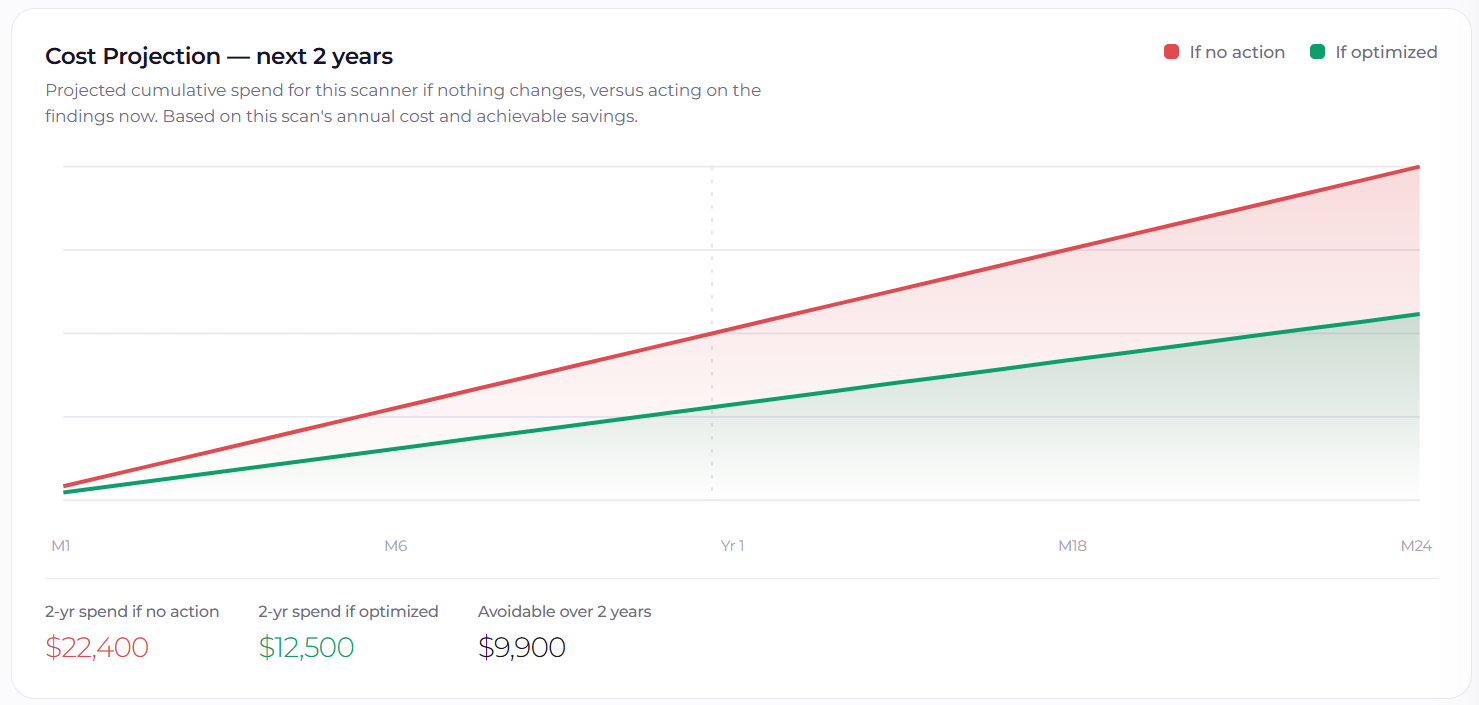
  • Two-year projection: cumulative spend if untouched versus remediated
Ghost infrastructure

Unattached EBS volumes, orphaned snapshot chains, incomplete S3 multipart uploads, stopped EC2 still billing root volumes, and zero-connection RDS instances.

Governance & tag drift

Untagged resources, environment drift, and cost-allocation tag gaps — useful input for governance and audit reviews.

Exposure & encryption

Public buckets, unencrypted volumes, publicly reachable RDS endpoints, and logging posture across the core service layers.

Scanning engines

Seven static-analysis passes over your metadata. Each one targets a specific class of waste.

Seven engines.
One read-only role.

Storage, compute, database, serverless, logging, and cross-service architecture — every pass runs from the same read-only role. Scroll to walk each one.

    7
    scanning engines
    1
    read-only role to connect
    0
    write permissions requested
    <3min
    to a full estate audit
    Spotlight

    Architecture Review — waste that hides between services

    Single-resource scanners look at one thing at a time. This pass reads across the account to catch spend that works correctly but wastes money by design: idle plumbing on an hourly meter (ALBs with no targets, idle NAT gateways, unattached Elastic IPs), missing S3/DynamoDB VPC gateway endpoints that route traffic through NAT, and over-provisioned ElastiCache or low-value CloudFront. Hard savings where a charge is provable; advisory flags where it isn't.

    Sample cross-service findings

    Idle load balancer · no targets
    $197/yr
    Idle NAT gateway
    $394/yr
    Unattached Elastic IPs · ×3
    $118/yr
    Missing S3 VPC endpoint
    NAT data ↓

    Need a specific AWS service audited? Tell us what to cover next.

    Inside the product

    The output is a report, not a chart. Every row is a resource, a dollar figure, and a dependency map.

    What the audit
    actually returns.

    Each finding carries a quantified annual cost, a blast-radius dependency check, and a concrete remediation. These are views from an actual assessment run.

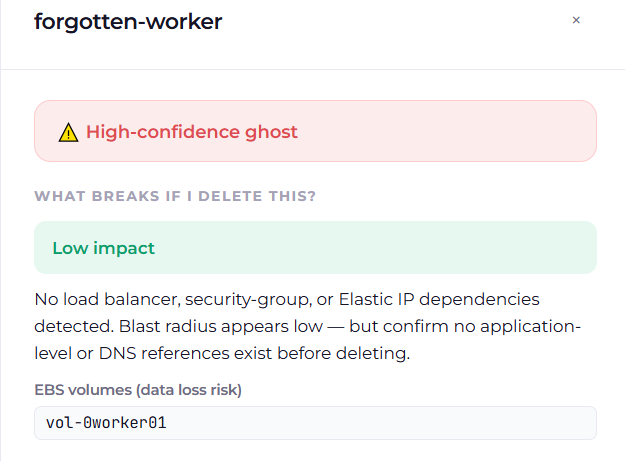
    ghosttrace · ec2 · instance detail
    EC2 instance detail panel showing a high-confidence ghost with a low-impact blast radius and an attached EBS volume flagged for data-loss risk.
    Blast radius

    “What breaks if I delete this?”

    Before you touch an instance, see the real dependencies — load balancers, security groups, Elastic IPs, and volumes that hold data — graded low to high impact from read-only signals.

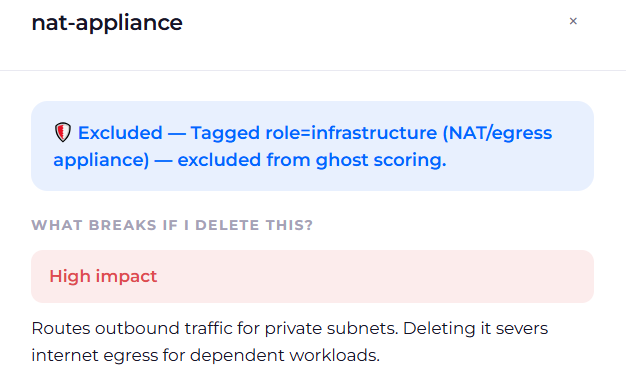
    ghosttrace · ec2 · nat-appliance
    EC2 panel showing a NAT appliance excluded from ghost scoring because it is tagged as infrastructure, with a high-impact blast radius warning that deleting it severs internet egress.
    Honest scoring

    Knows infra from ghosts

    Role inference and tags exclude NAT appliances, bastions, and DNS boxes from ghost scoring — and still warn you that deleting one severs egress for everything behind it.

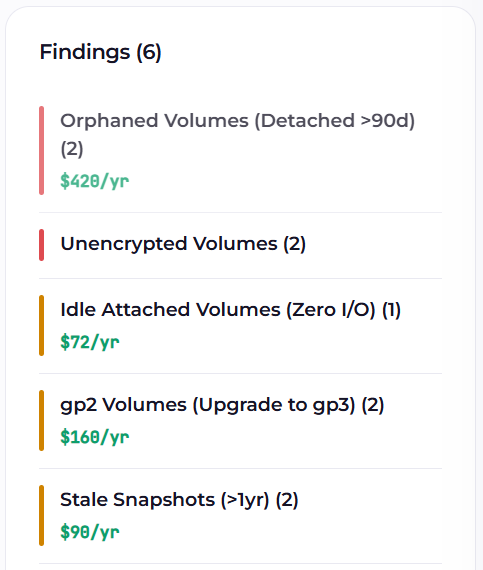
    ghosttrace · ebs · findings
    EBS findings list: orphaned volumes, unencrypted volumes, idle attached volumes, gp2-to-gp3 upgrade candidates, and stale snapshots, each with an annual dollar saving.
    Prioritised findings

    Ranked by dollars, not noise

    Orphaned volumes, idle disks, gp2→gp3 upgrades, and stale snapshots — each with the exact annual saving attached, highest impact first.

    ghosttrace · cost projection
    Two-year cost projection chart comparing cumulative spend if no action is taken versus if the findings are optimised, showing roughly ten thousand dollars avoidable over two years.
    2-year projection

    Act now vs. do nothing

    Each scanner plots cumulative spend if nothing changes against acting today — derived from the scan’s own annual cost and achievable savings, so the numbers tie out.

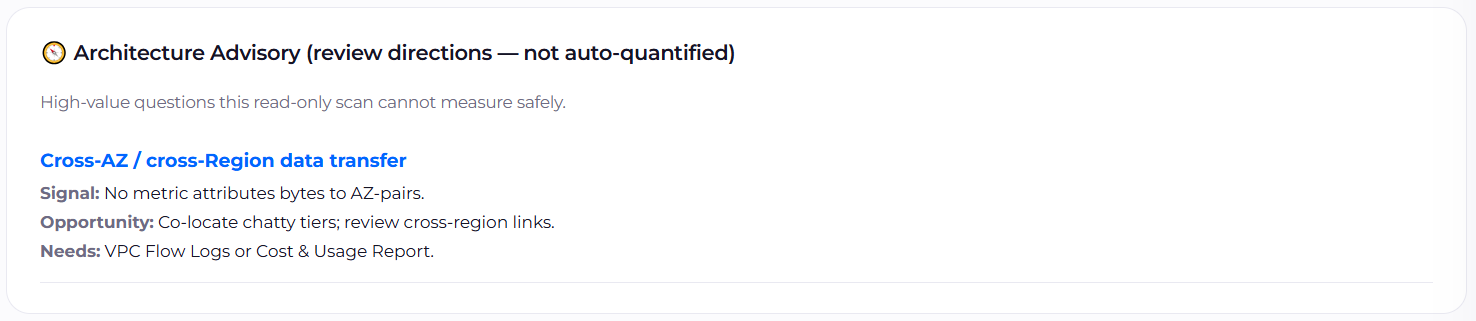
    ghosttrace · architecture · advisory
    Architecture advisory card describing cross-AZ and cross-region data transfer review directions that a read-only scan cannot measure safely, with the signal, opportunity, and data needed.
    Advisory layer

    Review directions, not guesses

    For questions a read-only scan can’t quantify — cross-AZ transfer, duplicate telemetry — we hand you the signal, the opportunity, and exactly what data would confirm it.

    Onboarding

    In and out. No footprint left behind.

    Four steps. Two minutes. Read-only throughout.

    Grant access with a scoped, read-only IAM role — no agents, no VPC peering, no data egress.

    01

    Generate tenant ID

    Sign up to issue a cryptographically unique ExternalID — your Confused-Deputy guard.

    02

    Deploy IAM role

    One-click CloudFormation stack, or paste the read-only policy manually.

    03

    STS handshake

    We assume the role via STS and verify read-only access is in place.

    04

    Savings audit

    Metadata collectors enumerate the estate and return a costed report in under 3 minutes.

    Security first

    Control plane only. Never your data.

    GhostTrace reads one thing: configuration metadata — resource settings, tags, attachment state, and CloudWatch metrics. That's the entire granted scope, so your file contents, database rows, and live sessions stay yours alone.

    Read-only metadata access Per-tenant ExternalID guard Temporary credentials, auto-expire within the hour Revoke anytime — delete the role
    Plans

    Pay for what you hunt. One month at a time — nothing recurring.

    Simple pricing. Pay per month.

    The S3 scanner is free — audit your estate and see the savings first. Then put those savings toward a paid month when you want the other scanners. Each plan is a one-time payment for one month. No auto-renewal, no subscription locked to your card.

    Free
    $0

    No card required.

    Start free
    • 3 scans / month
    • 1 AWS account
    • S3 scanner only
    Starter · Popular
    $19 / month

    For a single team.

    Get 1 month — $19
    • 25 scans / month
    • Up to 3 AWS accounts
    • All 7 scanners
    Growth
    $49 / month

    For growing teams.

    Get 1 month — $49
    • 75 scans / month
    • Up to 10 AWS accounts
    • All 7 scanners
    Business
    $99 / month

    For large estates.

    Get 1 month — $99
    • 200 scans / month
    • Unlimited accounts
    • Priority support

    Agency accounts and white-label reporting are coming soon.

    Typical first-scan recovery
    $0/ yr reclaimed

    A representative first scan: idle storage, ghost compute, and zero-connection databases turned into line-item savings, each with the exact annual figure attached.

    Unattached EBS $1180 Zero-conn RDS $730 Idle EC2 $480 S3 lifecycle $200
    Get started

    The waste was always there. Now it has a name and a dollar figure.

    Find the ghost infrastructure in your AWS estate.

    Connect a read-only role and get a deterministic, cost-quantified audit report in under three minutes.